
Act now
Address the vulnerability when a fix is a priority.
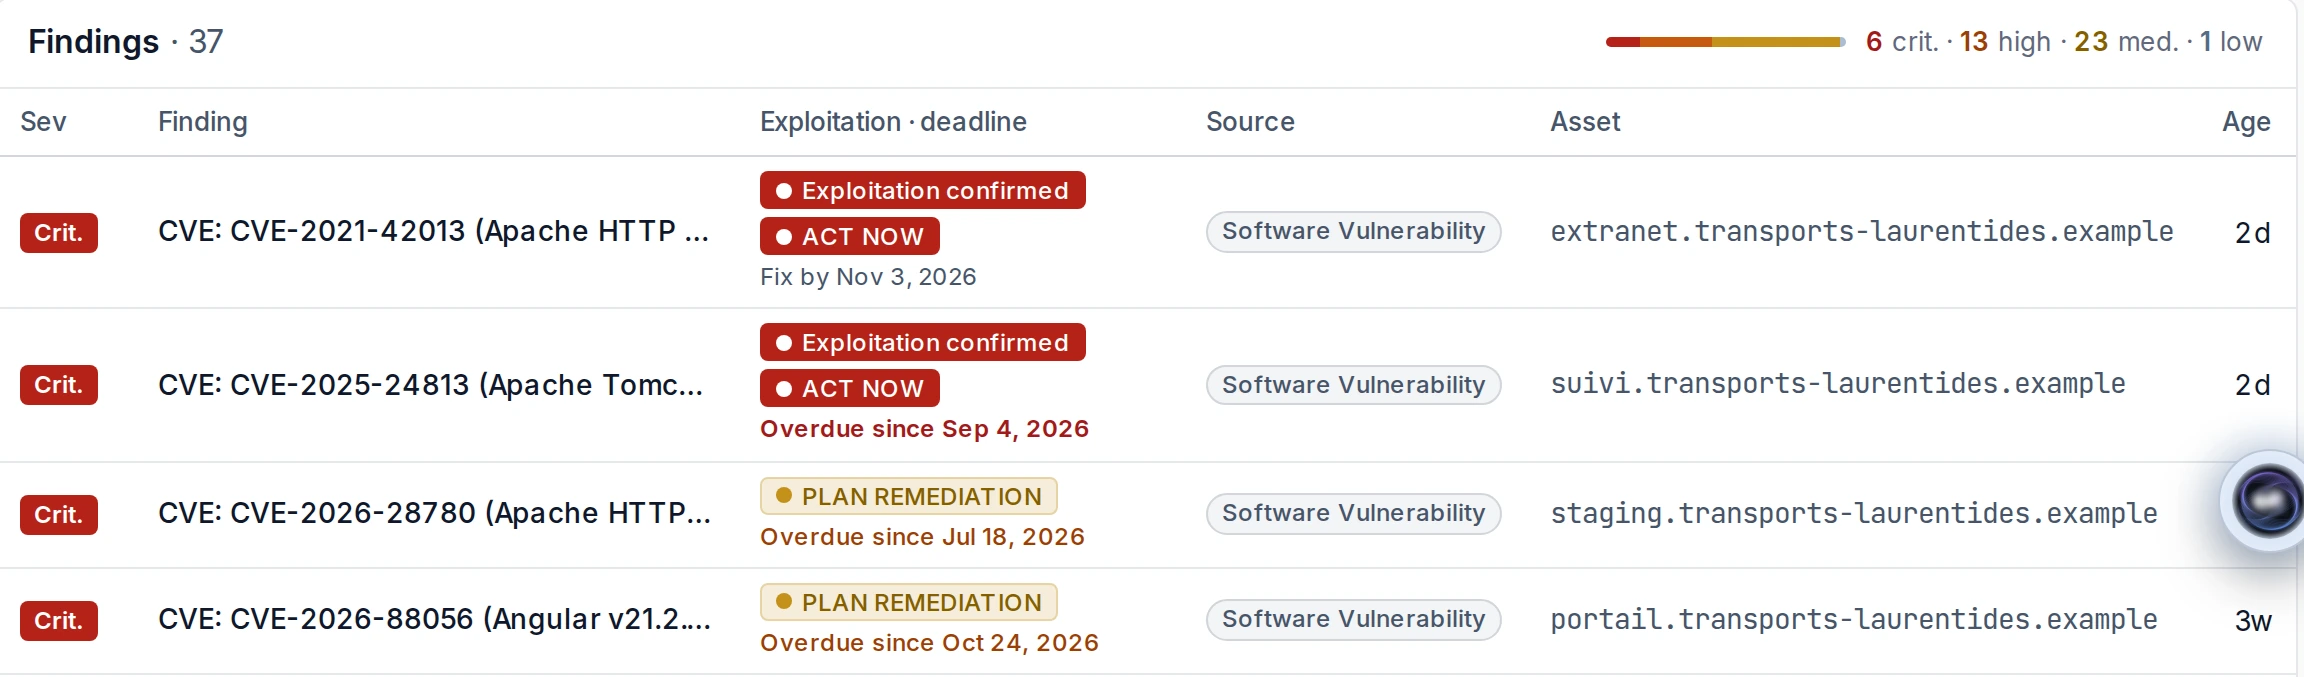
Predictra compares detected software versions with newly published vulnerabilities each day, without running another analysis or sending traffic to your servers.
Each day, detected software versions are compared with newly published vulnerabilities in the National Vulnerability Database (NVD) from the National Institute of Standards and Technology (NIST). No new analysis is run; this watch never closes a finding.
Each vulnerability is put into context to help your team decide what to address first.
Detected software versions are compared with NIST’s NVD database to flag known vulnerabilities (CVEs). For each vulnerability, Predictra also brings together its presence in the CISA KEV catalogue, exploitation likelihood from EPSS, and the product’s end-of-life status.
Useful information is brought together in a remediation sheet, so you can choose between acting now and scheduling the fix.
For each vulnerability (CVE), the sheet brings together vendor advisories, fixed versions, exploitation likelihood from EPSS, presence in the CISA KEV catalogue, and product end of life.
Address the vulnerability when a fix is a priority.
Organize remediation using the information available.
An alert is issued when the daily watch finds a new CVE, or when an analysis reveals a new, reappeared or more severe vulnerability.
No. The daily watch never closes a finding. A finding is closed automatically when a new analysis checks the target and no longer finds it. It is reopened if it reappears, and is never closed after an incomplete analysis.
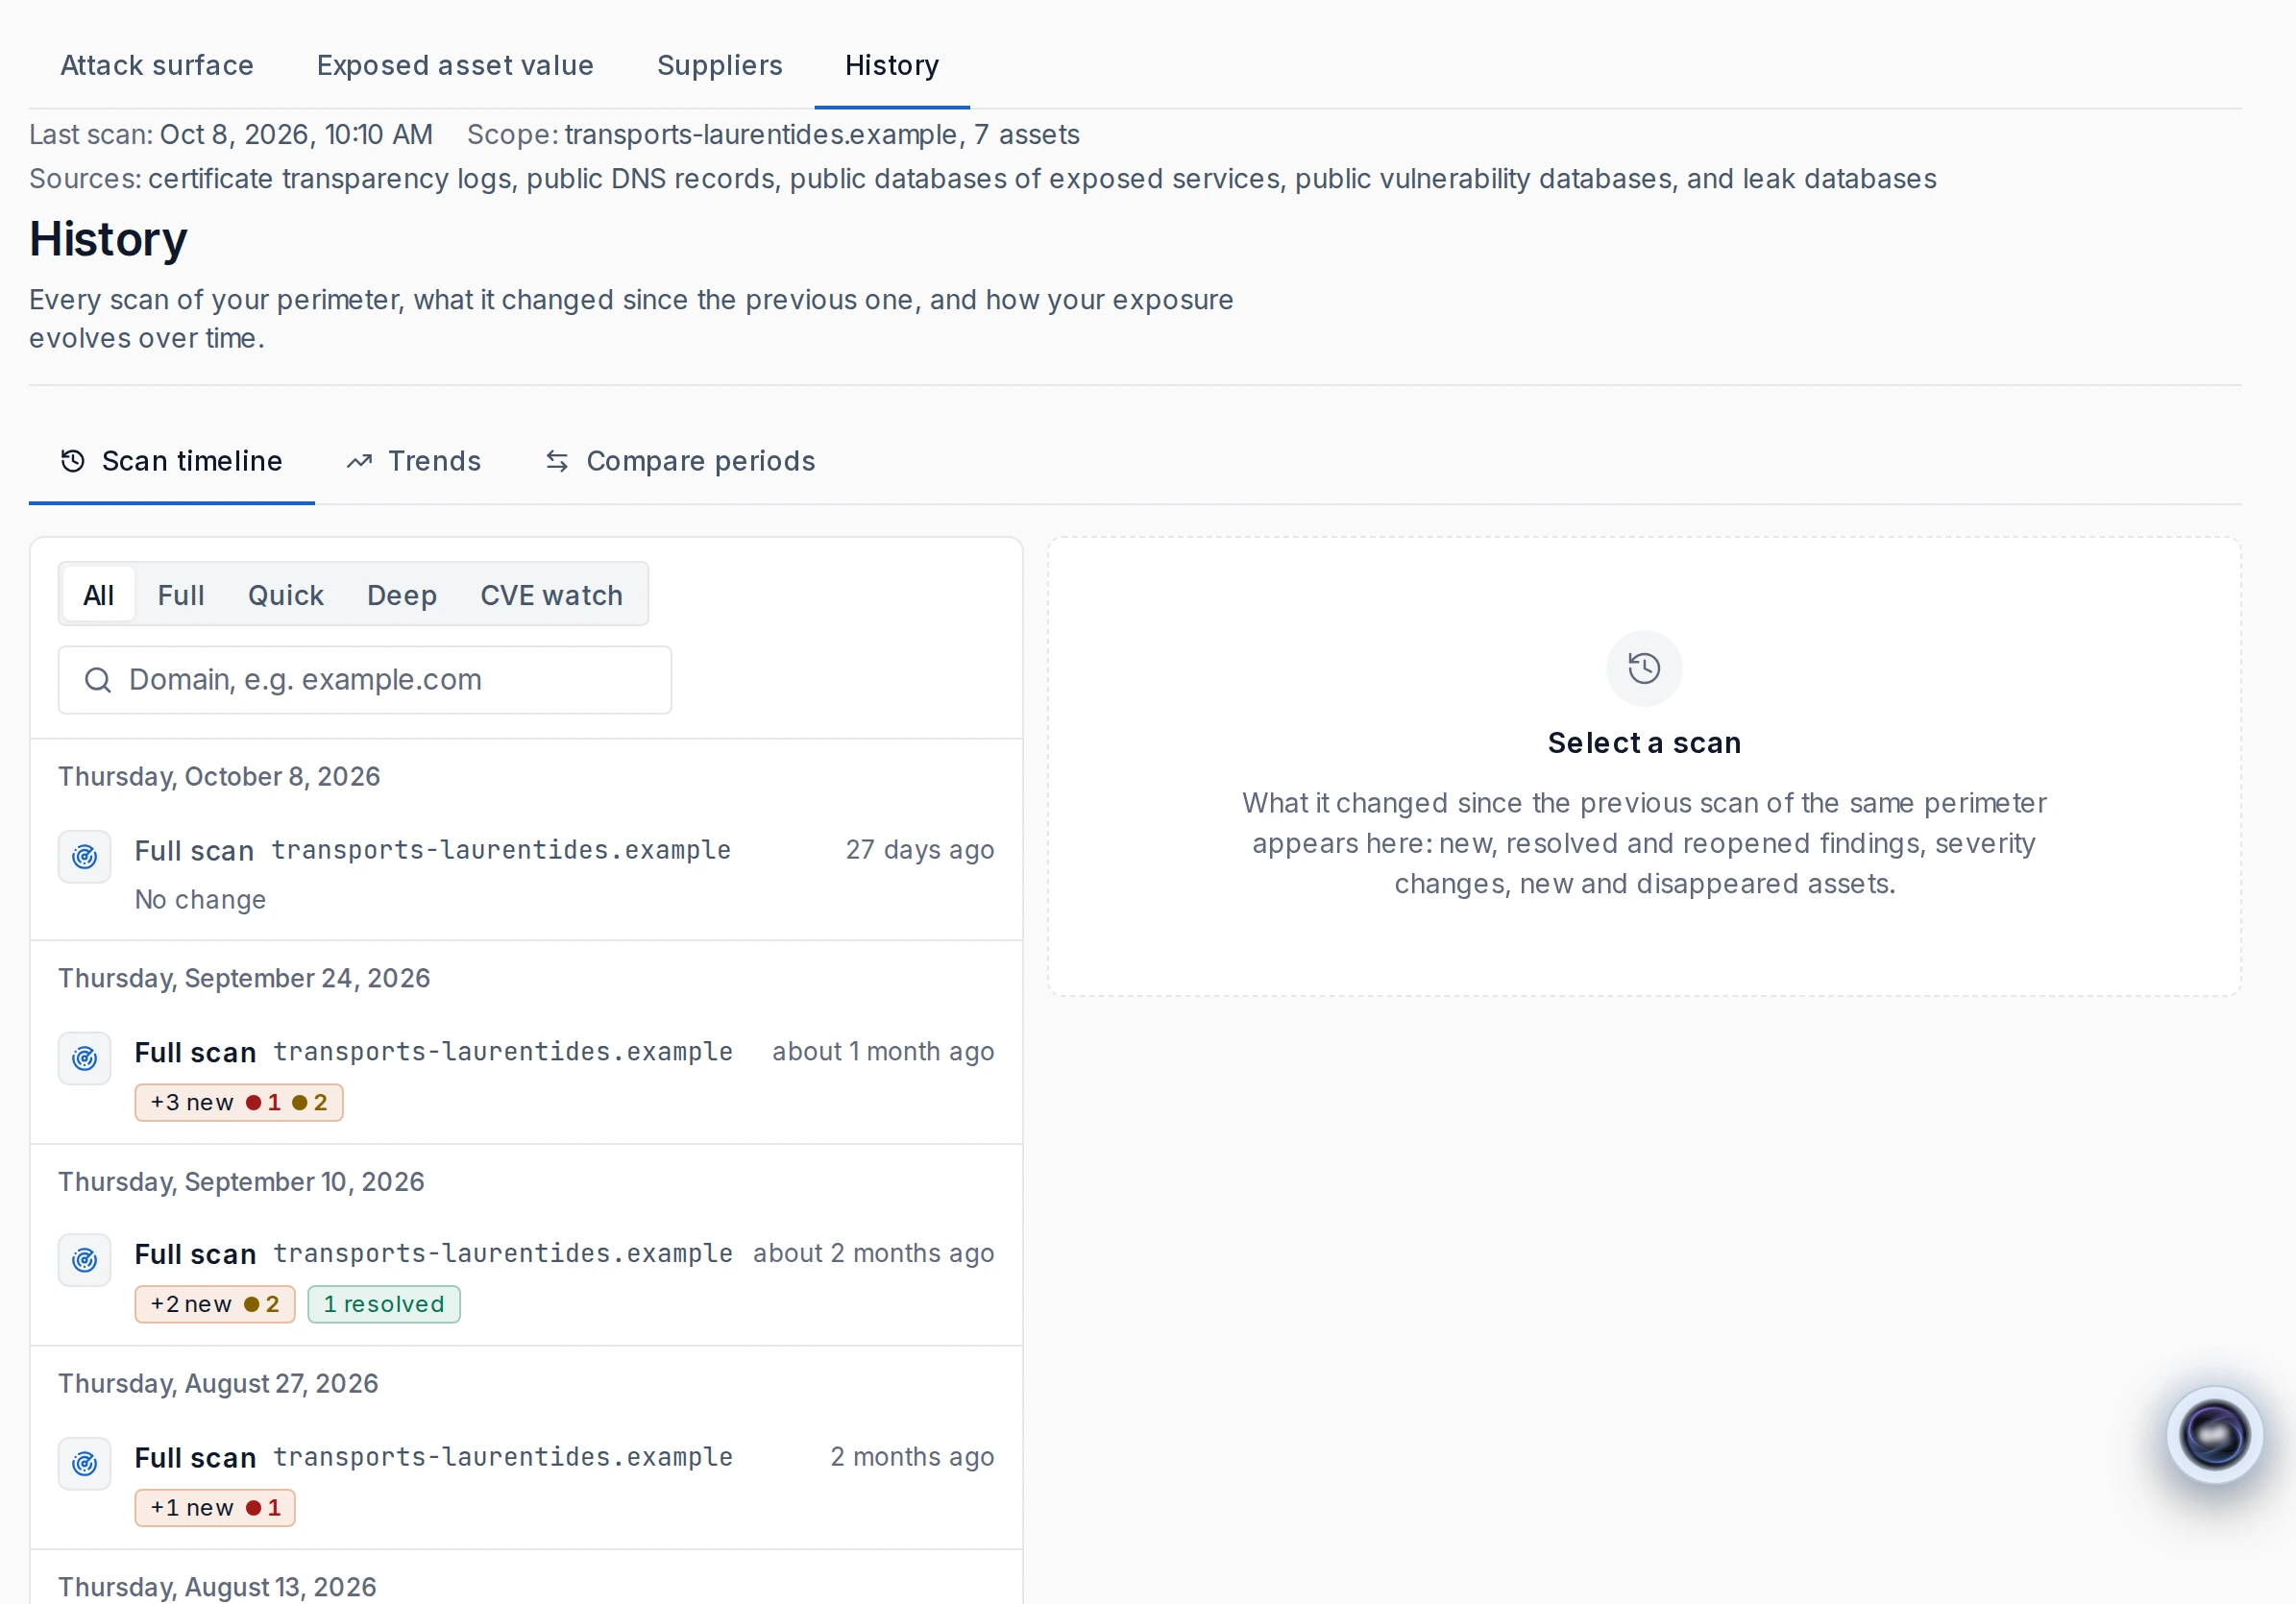
The watch relies on versions already detected and newly published vulnerabilities. It does not replace a new analysis.