
Threat intelligence
The threats affecting your organization, explained clearly
Predictra tracks threats affecting your organization using public sources and specialized intelligence sources.
Threat actor profile
Illustration — fictitious organizationSectorYour sector
CountryYour country
Generic techniques · MITRE ATT&CK
- Phishing
- Exploitation of exposed services
Link threats to decisions
Predictra brings together signals relevant to your organization and links them to vulnerabilities and remediation actions.
- Public sources and specialized intelligence sources
Average annual increase in ransomware incidents
“Based on our data, ransomware incidents have grown, on average, 26% year-over-year since 2021.” These are incidents known to the Centre for Cyber Security.
“Based on our data, ransomware incidents have grown, on average, 26% year-over-year since 2021.”
Dark web: monitor your keywords
Predictra searches for your names, brands and domains in dark web pages collected by its crawler.
- Names, brands and domains
- Collected .onion pages
What does Predictra check?
Monitoring of your keywords—names, brands and domains—in dark web pages (.onion sites) collected by our crawler.
Ransomware claims
Predictra tracks claims published by ransomware groups and alerts you if your domain matches a claimed victim.
- Critical alert when there is a match
How does the alert work?
Tracking of claims published by ransomware groups on their leak sites, using ransomware intelligence sources. If a ransomware group claims a victim whose domain matches one of yours, you receive a critical alert.
What are the limits?
No stolen data is downloaded: for a ransomware claim, only metadata is kept. A claim is not proof of an intrusion: an administrator confirms or dismisses it. A match based on the name alone is presented as a case to verify.
Threat actor profiles
Review profiles of threat actors active in your sector and country, with public sources and generic MITRE ATT&CK techniques.
- Sector and country
- Generic MITRE ATT&CK techniques
What sources support the profiles?
Profiles of threat actors active in your sector and country, based on public sources: MITRE ATT&CK, the CISA KEV catalogue, EPSS, a community threat actor knowledge base, ransomware and malicious infrastructure intelligence sources, and news feeds.
Threat actor profile
Illustration — fictitious organizationSectorYour sector
CountryYour country
Generic techniques · MITRE ATT&CK
- Phishing
- Exploitation of exposed services
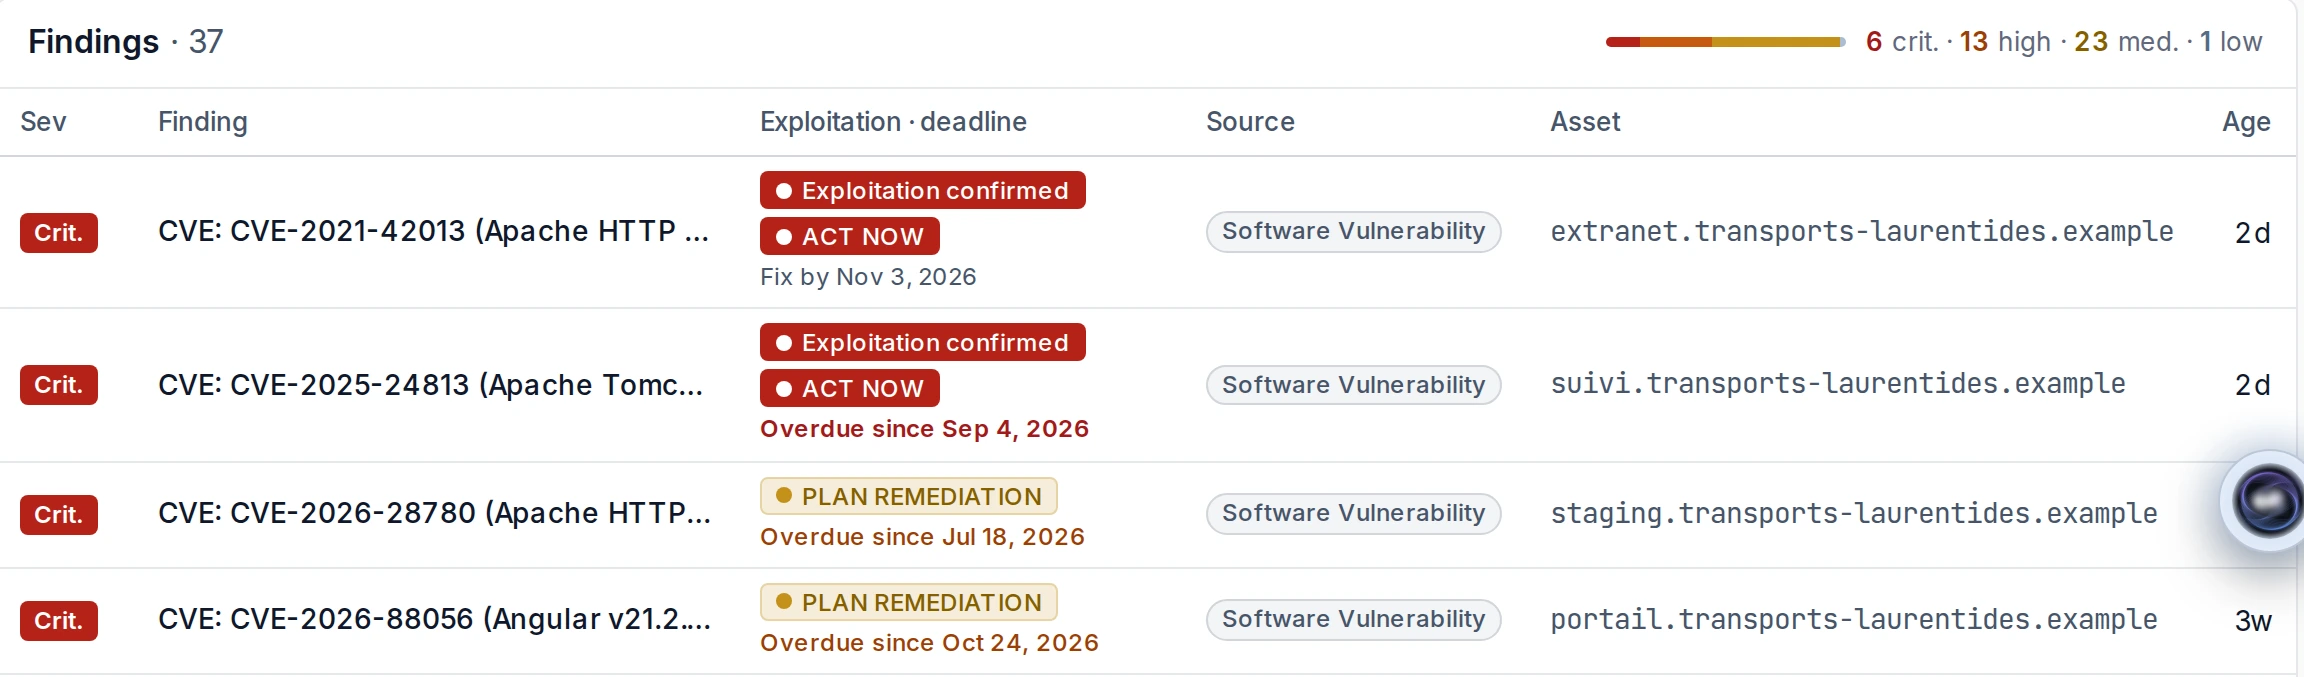
From threats to remediation
Remediation sheets bring together the information needed to understand a vulnerability and plan the appropriate action.
- Vendor advisories
- Fixed versions
- Exploitation probability (EPSS)
- CISA Known Exploited Vulnerabilities (KEV) catalogue
- Product end of life
What does a remediation sheet contain?
For each vulnerability (CVE): vendor advisories, fixed versions, exploitation probability (EPSS), presence in the CISA KEV catalogue and product end of life.
How are actions presented?
Vulnerabilities and actions are presented with the usual entry point used by ransomware groups for those actions.
Signals to verify
The results help you decide, but a ransomware claim must be confirmed or dismissed by an administrator.
- The dark web sites explored are selected by Predictra
- A claim is not proof of an intrusion
- Assistant responses may contain errors
What Predictra does not do
Only dark web sites selected by Predictra are crawled. No stolen data is downloaded: for a ransomware claim, only metadata is kept. A claim is not proof of an intrusion: an administrator confirms or dismisses it.