
Vendors and third parties
Monitor the external exposure of your vendors and third parties
Predictra tracks your vendors from public data. See their passive posture, your criticality and key signals; active testing requires the vendor’s authorization.
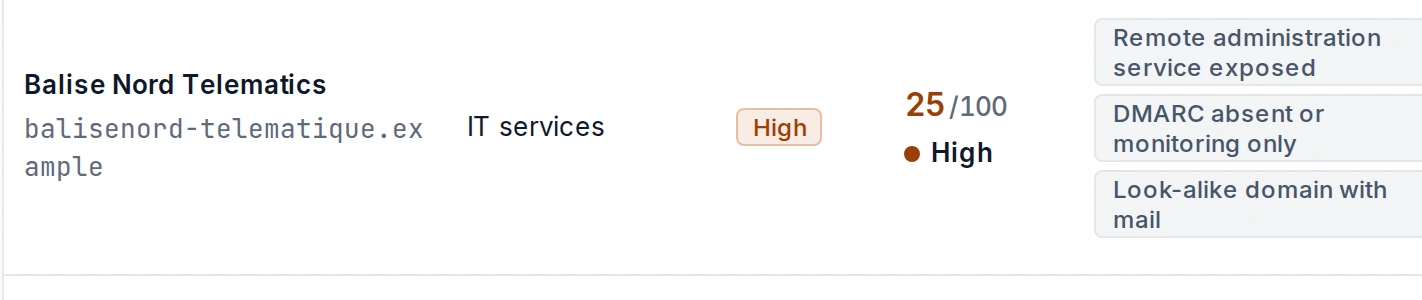
A passive view of your third parties
External posture is calculated from public data. Your organization’s criticality remains distinct from the vendor’s score.
- Passive posture calculated from public data.
- Criticality assigned by your organization.
- Key signals gathered in the vendor profile.
A vendor, its signals and authorization
Sample data| Vendor | Category | Criticality | Your score | Main signals | Authorization |
|---|---|---|---|---|---|
| Balise Nord Telematicsbalisenord-telematique.example | IT services | High | 25/100High | Remote administration service exposedDMARC absent or monitoring onlyLook-alike domain with mail | |
| FretPlan Solutionsfretplan.example | Other software-as-a-service | Critical | 20/100Moderate | No signal |
Turn a list into ongoing follow-up
Import the vendors and third parties you want to follow, record their criticality, then review profiles refreshed each week.
- Import your vendor and third-party list.
- Record how important each vendor is to your organization.
- See the score, signals and authorization in one profile.
Observing is not testing
Passive follow-up is not authorization. The vendor concerned must authorize active testing; proof of domain control and a signed letter remain required according to the analysis level.
- Passive posture comes from public data.
- Following a vendor does not authorize testing it.
- Domain control and authorization frame active analyses.
What does vendor authorization mean?
A client mandate or an MSP’s authorization never replaces authorization from the vendor concerned. Active testing requires that vendor’s authorization, proof of domain control and the signed letter appropriate to the analysis level.
Your clients’ third parties, in your portfolio
A managed service provider (MSP) can follow its clients’ vendors and vendors shared by several clients. Vendor authorization remains required for active testing.
- Vendors of the MSP’s clients.
- Vendors shared by several clients.
- Vendor authorization required for active testing.
See how to follow your vendors
Request a presentation of the platform. For your domain, the free scan remains a passive assessment.