
01
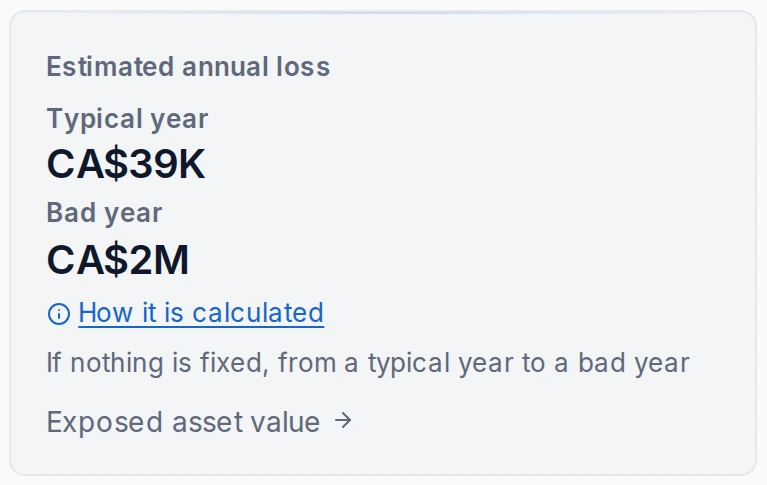
The amount
A range: a typical year and a bad year.
Possible annual loss
Example Inc. · Canadian dollars
Typical year$20,000
Bad year$300,000
Predictra analyzes what your organization exposes online, with no agent to install. You get the possible annual loss as a dollar range and a plan ranked by the loss each fix removes.
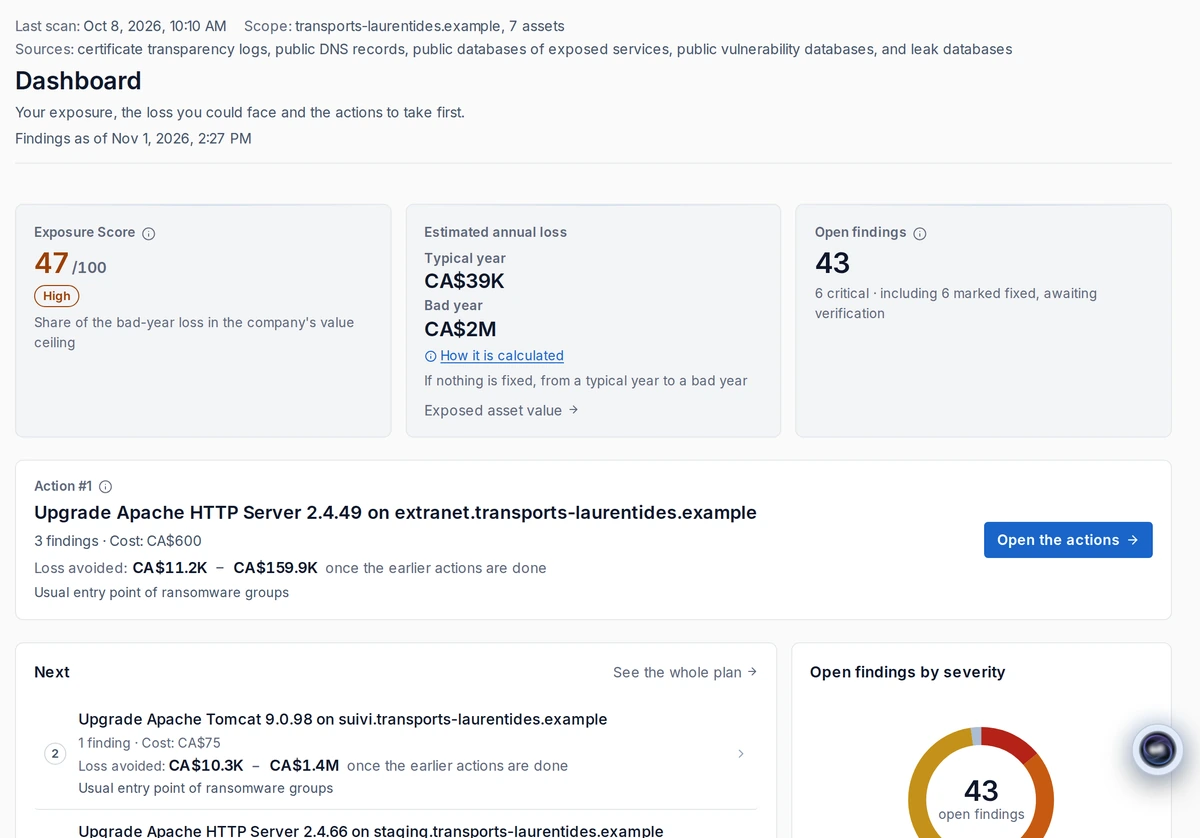
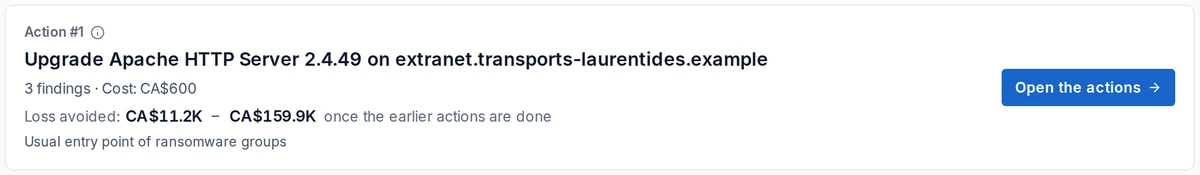
Each finding becomes a decision.
CVE-2021-42013Apache HTTP Server 2.4.49CVE-2025-24813Apache Tomcat 9.0.98CVE-2026-28780TLS · port 443CVE: vulnerability identifier. TLS: secure connection.
Sample dataA range: a typical year and a bad year.
Example Inc. · Canadian dollars
The loss removed sets priorities. When the effect is equal, the less costly action comes first.
Every number can be traced.
Remote access gateway affected by an actively exploited vulnerability · vpn.example.com
Problem The gateway uses a version affected by a known vulnerability listed in CISA’s Known Exploited Vulnerabilities (KEV) catalog.
Risk An attacker could enter the network, then deploy ransomware or take data.
Impact Possible annual loss for this asset: $8,000 (typical year) to $290,000 (bad year).
Action Install the fixed version; restrict access (multi-factor authentication, allowed addresses); check connections since the vulnerability was published. 2 to 4 hours · medium difficulty.
Fix and restrict the remote access gateway
$7,000 – $200,000
Typical year — bad year
Predictra model — public sources
Reset the 12 accounts found in infostealer logs and enable multi-factor authentication for email
$5,000 – $35,000
Typical year — bad year
Predictra model — public sources
Update the site content management system (2 high-severity vulnerabilities)
$3,000 – $30,000
Typical year — bad year
Predictra model — public sources
example.com
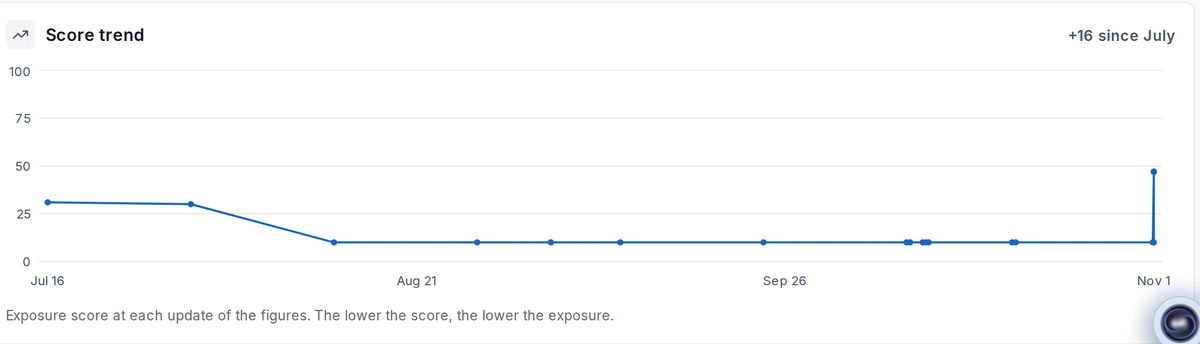
Predictra tracks changes and new vulnerabilities.
Services, versions and certificates.
Known and exploited.
Leaked credentials and infostealer logs.
Checks against spoofing.
Registered variants.
Passive third-party posture.
Threat actors and claims.
Based on your profile.
Changes, alerts and tickets.
Outdated web server software on the extranet and tracking sites is the main exposure.
Outdated web server software on the extranet and tracking sites is the main exposure; a short, low-cost plan could remove most of the estimated annual loss.
Your data, your permissions. The Assistant only reads, using exactly your permissions.
Answers may contain errors. Check important information before acting on it.
Answers are generated automatically from your Predictra data. Like any automatically generated text, they may contain errors. Check important information before acting on it.
An amount and a plan for management. What you need to prepare a cyber insurer’s questionnaire.
For small businesses
A report with dollar figures for each client to justify the work, using your own rates.
For MSPsSolutions Predictra inc., based in Laval, Canada.
Proof of domain control; signed authorization for testing.
Proof of domain control before any active analysis, a signed authorization letter for vulnerability testing, and an administrator can stop an analysis at any time.
App-based multi-factor authentication and an access log your administrators can review.
App-based two-factor authentication and an access log your administrators can consult. Predictra staff open a stated, time-limited access session to view an organization’s data; only administrative operations take place outside a session.
Your current exposure, not an announcement of an attack.
Security and trustA one-time passive assessment of your domain using public sources. After you confirm your email, you see the main findings and a preview of the possible annual loss. The report follows by email.
No. Predictra analyzes what is visible from outside your organization. There is no agent to install.
No. You first prove that you control the domain. Vulnerability testing requires a signed authorization letter. The owner or an administrator can stop a test at any time.
They are never stored: as soon as they are collected, they are replaced with attributes useful for remediation and a non-reversible hash. Predictra never uses a leaked credential to log in or check whether it works.
Yes. The managed service provider (MSP) console groups clients, sets each client’s analysis frequency and sends alerts to the team. Each client must have a signed mandate and a verified domain.
Passive assessment. Report sent by email.